

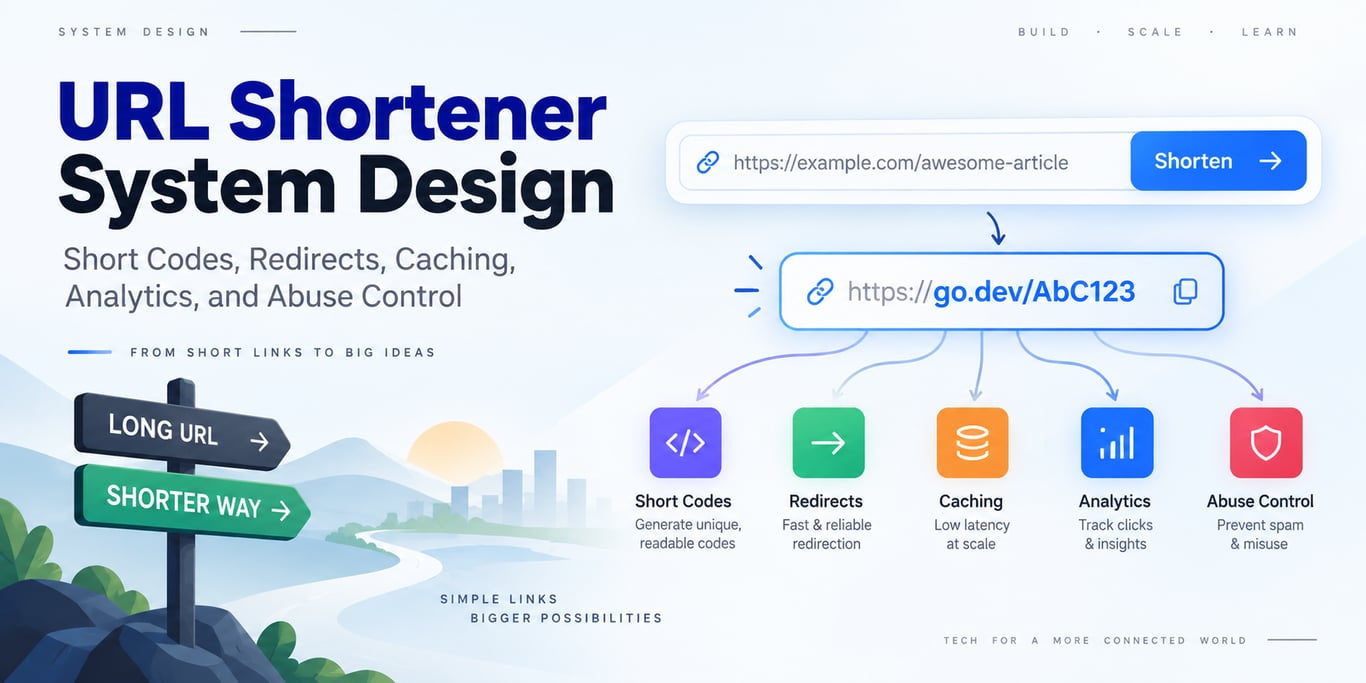
A URL shortener has two very different paths:
The create path writes mappings. The redirect path is read-heavy and must stay extremely simple.
Data Model
A minimal mapping can contain:
short_code
target_url
owner_id
created_at
expires_at
status
Use a unique constraint on short_code so collisions can never silently overwrite another URL.
Generate Short Codes
Two common approaches are:
- encode a unique numeric ID using a compact alphabet such as Base62
- generate cryptographically random codes and retry on the rare collision
Sequential IDs are simple but can expose creation volume/predictable neighboring codes. Random codes reduce predictability but require collision handling.
Optimize the Redirect Hot Path
Redirects usually dominate traffic. Cache popular short_code → target_url mappings close to the application or edge, while the durable database remains authoritative.
For immutable links, CDN/edge caching can remove substantial origin load.
Choose Redirect Semantics Intentionally
HTTP 301 means permanent redirect and can be cached aggressively by clients/intermediaries. 302 means the resource is temporarily at another URI.
If users can edit a short link's destination, a temporary redirect is often safer because a permanently cached destination can be difficult to change reliably.
Move Analytics Off the Redirect Path
Do not block the user while synchronously updating analytical counters.
redirect → publish click event → analytics consumers
This keeps redirect latency low and lets analytics scale independently.
Abuse and Security
URL shorteners can hide phishing/malware destinations. Add controls appropriate to the product:
- authenticated/rate-limited creation
- URL validation
- abuse reporting and disabling
- domain/reputation checks where justified
- limits on automated bulk creation
Avoid automatically server-fetching arbitrary target URLs unless SSRF protections are designed for it.
Final Takeaway
A scalable URL shortener keeps the redirect path tiny: resolve short code, use cache when possible, return a redirect, and process analytics asynchronously. The interesting engineering is collision-safe keys, cache behavior, redirect semantics, durability, and abuse control.
References

Discussion (0)